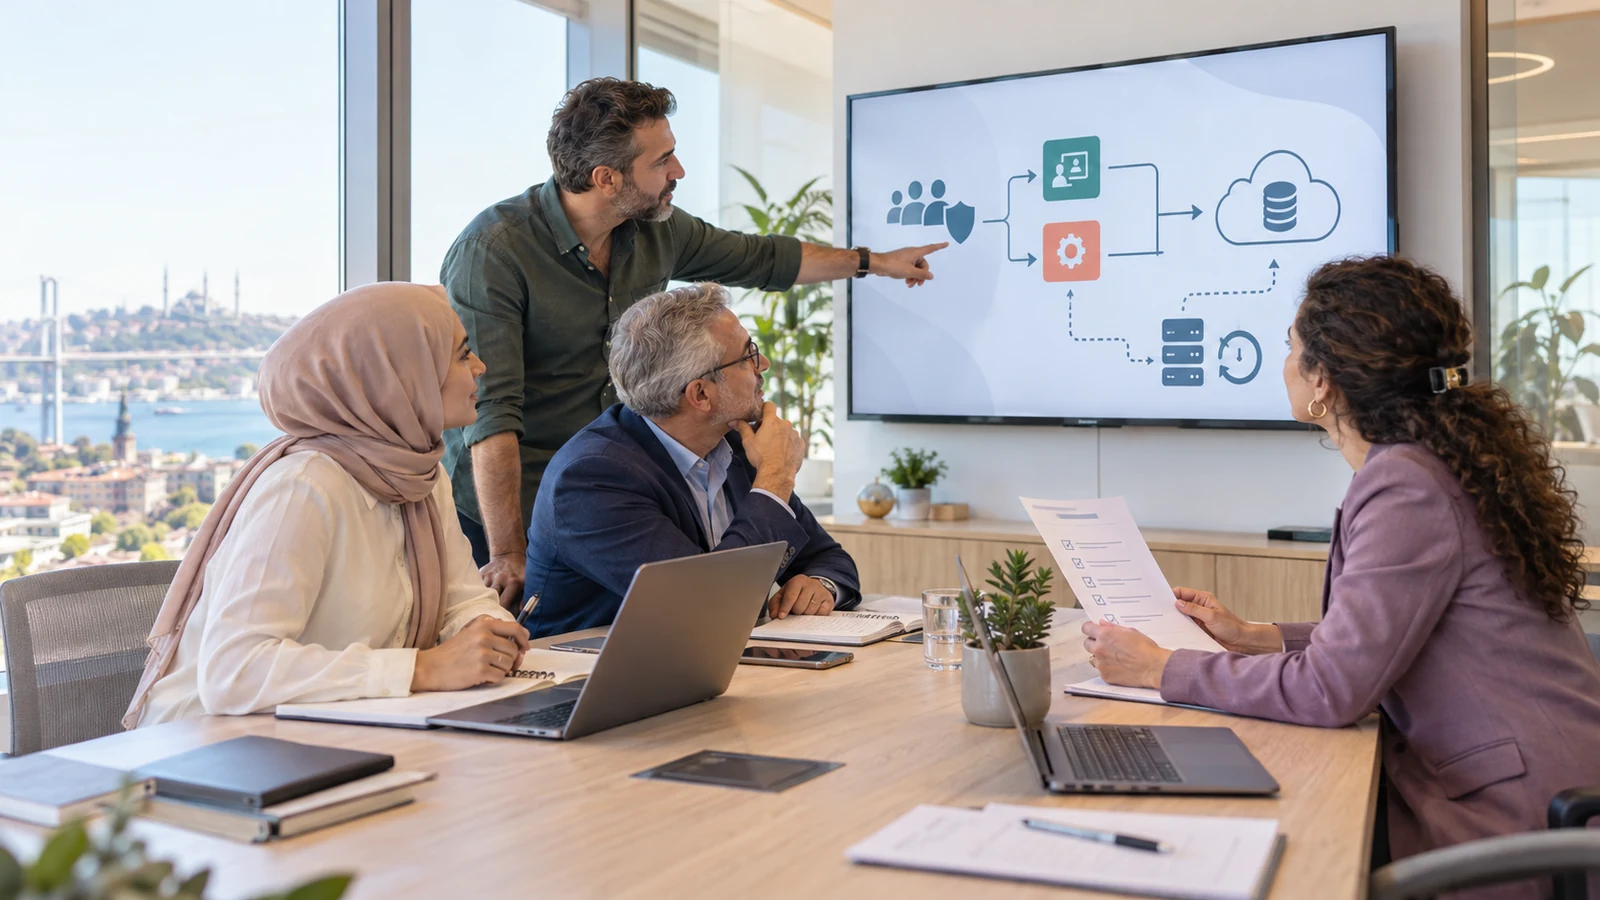
Begin with data and responsibility
List the customer, financial, employee, document and operational data moving through each system. For every flow, identify the business owner, technical owner, authorised users, purpose and retention expectation. Security becomes actionable when responsibility is attached to a real process rather than a generic policy.
Apply least privilege to daily work
Roles should reflect what a user needs to view, create, approve, export or administer. Separate routine work from high-impact permissions and review accounts when responsibilities change. Service accounts and integration credentials need named ownership, protected storage and rotation rules just as human accounts do.
Monitor integrations and important actions
Authentication failure, unusual export, repeated API error, rejected record and privileged configuration change should not disappear inside separate logs. Define which events are monitored, who receives an alert, how quickly the team responds and how the decision is recorded. Traceability supports both security and operational quality.
Plan recovery as a business capability
Backups are useful only when the organisation knows what is protected, how often it is captured, where copies are kept and how restoration is tested. Set recovery priorities for critical processes and document temporary manual procedures for periods when a system or connection is unavailable.
Test people, technology and suppliers together
A continuity exercise should include business teams, IT, software providers and other relevant partners. Use realistic scenarios such as unavailable authentication, corrupted synchronisation, delayed e-document transmission or lost network access. Record lessons, update ownership and repeat the test after material changes.